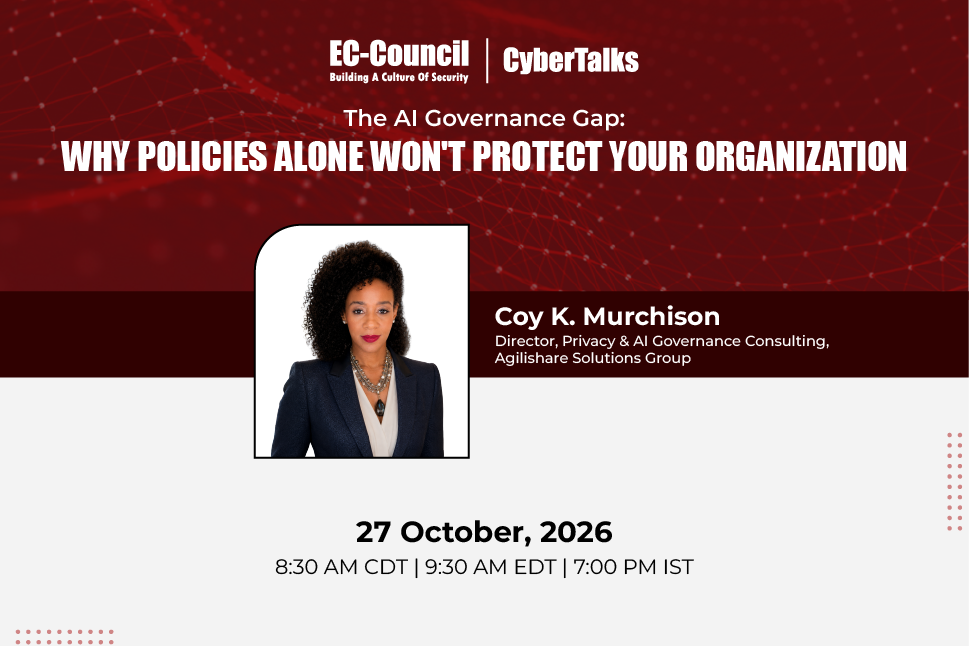
Date: October 27, 2026
Time: 8:30 AM CDT | 9:30 AM EDT | 7:00 PM IST
Topic: The AI Governance Gap: Why Policies Alone Won’t Protect Your Organization
Register Now
Abstract: Having an AI policy is not the same as having AI governance. As artificial intelligence becomes embedded across enterprise operations, organizations are discovering that documentation alone cannot substitute for the structured accountability, cross-functional oversight, measurable controls, and lifecycle monitoring that effective AI governance demands.
This webinar takes a practical, operational look at what separates AI policy from true AI governance. Designed for privacy, compliance, cybersecurity, legal, risk, and technology professionals, the session provides a clear path for building governance programs that move beyond compliance checkboxes and demonstrate genuine organizational accountability and regulatory readiness.
One of the most persistent governance gaps lies in how organizations treat governance as a documentation exercise rather than an operational discipline. Across every industry, AI is being implemented at speed while governance frameworks lag behind. Closing that gap requires accountability structures, documented decision-making processes, oversight mechanisms, and evidence of responsible AI management.
Privacy professionals bring a distinct advantage to this challenge. Established disciplines, such as privacy by design, privacy impact assessments, data protection impact assessments, and risk assessments, already provide the operational foundations that AI governance requires. When applied to AI, these tools help organizations identify and manage risk, document governance decisions, prepare for audits, and stay ahead of evolving regulatory expectations.
Participants will leave this session equipped with actionable strategies to embed governance into their AI programs, support responsible innovation, and build the long-term organizational resilience that regulators and stakeholders increasingly expect.
Key Takeaways:
 Coy K. Murchison, Director, Privacy & AI Governance Consulting at Agilishare Solutions Group
Bio: Coy K. Murchison is a privacy and AI governance leader and Director of Privacy & AI Governance Consulting at Agilishare Solutions Group. With more than 17 years of experience in privacy and governance, her multidisciplinary work spans law, healthcare, risk, emerging technology, and the challenge at the center of modern AI governance: translating principles and policy into accountable, operational practice.
Coy holds a Juris Doctor from Florida Coastal School of Law and an MBA in Healthcare Administration from Texas Woman’s University. She is certified in Healthcare Privacy and Security (CHPS) by AHIMA and is a Certified ScrumMaster (CSM).
Her multidisciplinary background informs a governance approach designed to be legally sound, operationally executable, and resilient under real-world regulatory and organizational complexity.
She is the author of two white papers on artificial intelligence governance: Artificial Intelligence and the Privacy Governance Model, which defines a strategic framework for embedding privacy into enterprise AI governance, and Enterprise AI Governance Beyond Traditional IT Models, which examines the need for AI governance to extend beyond traditional technology structures through enterprise accountability and cross-functional oversight.
Together, her work advances a practical approach to moving AI governance from policy to accountable, enterprise-wide practice. Her career includes architecting the nation’s first medical-device governance program to centralize all components of privacy and security within a unified operating model at Texas Health Resources. She also built and operationalized a comprehensive privacy program spanning more than 300 clinics, establishing the governance structures, processes, tools, accountability mechanisms, and workforce practices necessary to embed privacy into day-to-day operations.
These experiences reflect a career spent turning regulatory requirements and governance principles into functioning operational systems. Today, she brings that same approach to enterprise AI governance—integrating traditionally siloed functions, establishing clear accountability, assessing risk before deployment, documenting decisions, and building governance that can be demonstrated, not merely declared.
- Understanding the critical distinction between AI policy, compliance obligations, and operational governance.
- Recognizing why AI governance programs fail even when policies are well-written and leadership is supportive.
- Identifying the foundational building blocks required for a scalable enterprise AI governance program.
- Establishing clear governance roles, accountability structures, decision-making authority, and cross-functional oversight.
- Creating governance artifacts that demonstrate organizational maturity and support regulatory readiness.
- Applying PIAs and DPIAs as practical governance tools that embed accountability and risk documentation across the AI lifecycle.
- Conducting AI-focused PIAs and DPIAs that address data flows, lawful processing, automated decision-making, third-party AI risks, and human oversight requirements.
- Embedding governance into every stage of the AI lifecycle rather than applying it as a one-time compliance activity.
- Evaluating organizational readiness to meet evolving AI regulations and governance expectations.
Coy K. Murchison, Director, Privacy & AI Governance Consulting at Agilishare Solutions Group
Bio: Coy K. Murchison is a privacy and AI governance leader and Director of Privacy & AI Governance Consulting at Agilishare Solutions Group. With more than 17 years of experience in privacy and governance, her multidisciplinary work spans law, healthcare, risk, emerging technology, and the challenge at the center of modern AI governance: translating principles and policy into accountable, operational practice.
Coy holds a Juris Doctor from Florida Coastal School of Law and an MBA in Healthcare Administration from Texas Woman’s University. She is certified in Healthcare Privacy and Security (CHPS) by AHIMA and is a Certified ScrumMaster (CSM).
Her multidisciplinary background informs a governance approach designed to be legally sound, operationally executable, and resilient under real-world regulatory and organizational complexity.
She is the author of two white papers on artificial intelligence governance: Artificial Intelligence and the Privacy Governance Model, which defines a strategic framework for embedding privacy into enterprise AI governance, and Enterprise AI Governance Beyond Traditional IT Models, which examines the need for AI governance to extend beyond traditional technology structures through enterprise accountability and cross-functional oversight.
Together, her work advances a practical approach to moving AI governance from policy to accountable, enterprise-wide practice. Her career includes architecting the nation’s first medical-device governance program to centralize all components of privacy and security within a unified operating model at Texas Health Resources. She also built and operationalized a comprehensive privacy program spanning more than 300 clinics, establishing the governance structures, processes, tools, accountability mechanisms, and workforce practices necessary to embed privacy into day-to-day operations.
These experiences reflect a career spent turning regulatory requirements and governance principles into functioning operational systems. Today, she brings that same approach to enterprise AI governance—integrating traditionally siloed functions, establishing clear accountability, assessing risk before deployment, documenting decisions, and building governance that can be demonstrated, not merely declared.