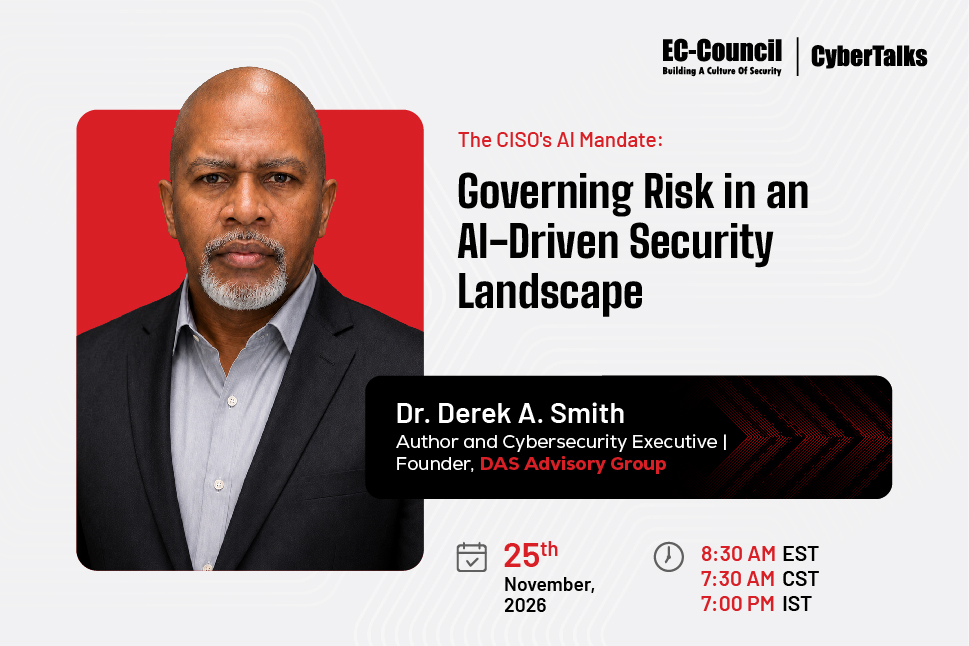
Topic: The CISO’s AI Mandate: Governing Risk in an AI-Driven Security Landscape
Abstract: The integration of AI into security operations is no longer optional. From automated threat detection and accelerated incident response to agentic systems capable of independent decision-making, AI is reshaping what the CISO role demands. The challenge is not whether to adopt AI, but how to do so in a way that introduces governance, accountability, and control alongside capability.
This webinar examines the AI mandate facing today’s CISOs, exploring how to build governance frameworks that make AI adoption both powerful and defensible. The session covers the risk dimensions unique to AI, including data exposure, model behavior, agentic autonomy, hallucinations, and reliance on third-party AI systems. It also addresses how these risks can be managed within a structured governance program.
The discussion will examine how AI is changing the security operations center (SOC), moving security operations from rule-based automation toward increasingly autonomous workflows, and what this means for the balance between AI decision-making and human oversight. Attendees will leave with a leadership perspective on governing AI as a strategic capability, not just a tool, one that strengthens cyber resilience while maintaining the trust, transparency, and auditability that enterprise and regulatory expectations demand.
Key Takeaways:
- How the CISO’s role is evolving to encompass AI governance and AI-driven security operations
- The emerging risk dimensions that AI introduces, including model risk, agentic autonomy, hallucinations, and third-party AI dependencies
- How to design AI governance frameworks that align innovation, security, compliance, and business value
- How agentic AI is reshaping SOC operations toward autonomous investigation, response, and decision-making
- Where human-in-the-loop controls remain essential and how to define the right balance between AI autonomy and human oversight
- Building trust, accountability, transparency, and auditability into AI-driven security systems from the outset
- How security leaders can position AI as a strategic driver of cyber resilience rather than a tactical automation layer
Speaker:
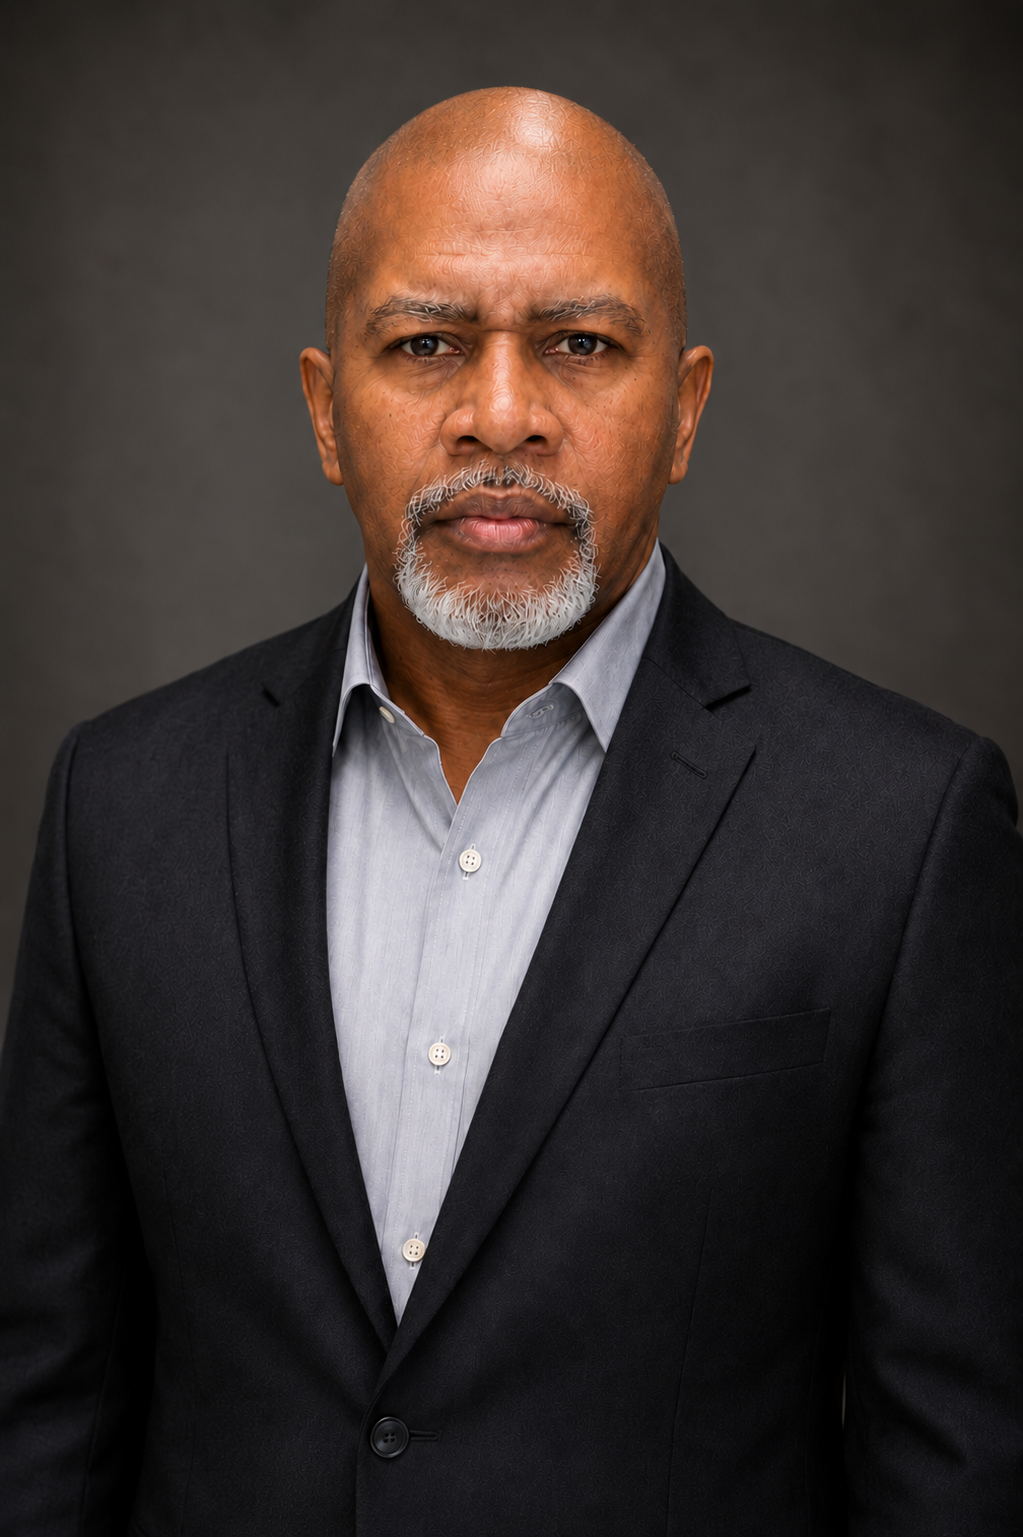 Dr. Derek A. Smith, Author and Cybersecurity Executive | Founder, DAS Advisory Group
Bio: Dr. Derek A. Smith is a cybersecurity executive and AI governance strategist with more than 30 years across federal, military, and academic environments. He served as a deputy director on the U.S. Department of Homeland Security’s HART biometric identification program and has led security and technology initiatives at the IRS, Booz Allen Hamilton, and beyond. He is the author of The Defensible AI Program: A Leader’s Playbook to Stand Up, Run, and Defend AI Governance — and Adopt AI With Confidence (a #1 Amazon New Release) and The AI-Powered Defender. As Cybersecurity Program Director at Virginia University of Science & Technology and founder of DAS Advisory Group, he helps agencies and enterprises govern AI with confidence. He holds a Doctor of Strategic Leadership and numerous industry certifications, including CCISO.