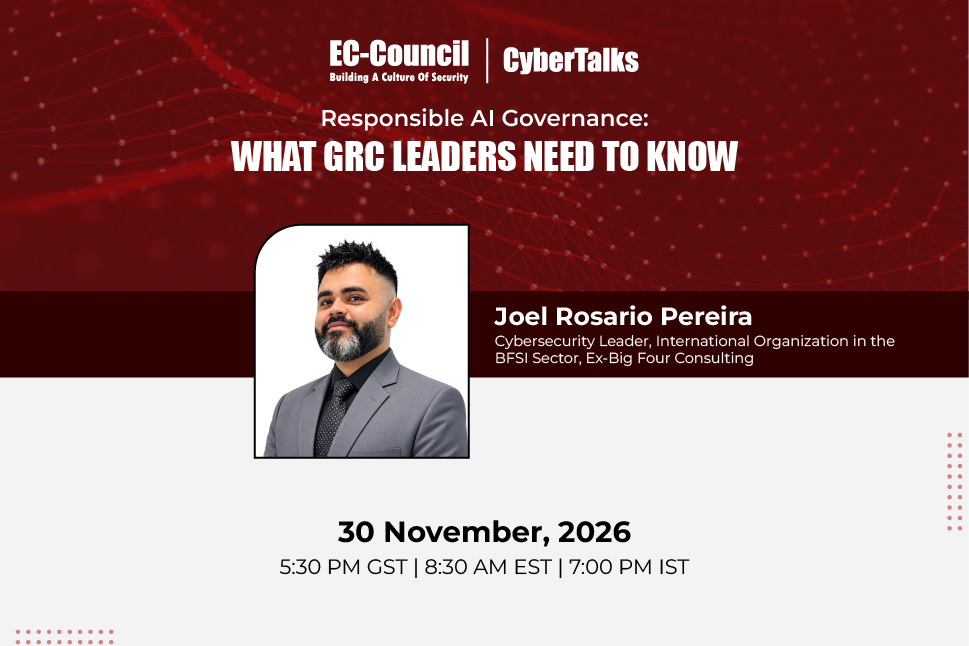
Topic: Responsible AI Governance: What GRC Leaders Need to Know
Abstract: AI governance is no longer a peripheral consideration for GRC leaders. As organizations move from isolated AI pilot use cases to enterprise-wide deployment, AI systems introduce risks such as data privacy concerns, model bias, lack of transparency, reliability challenges, and third-party dependencies. These risks require the same structured oversight that mature GRC programs apply to other enterprise risks.
This webinar examines what responsible AI governance looks like in practice for security and GRC leaders. It explores how AI-specific risks can be assessed, classified, and managed within existing enterprise governance structures. Moreover, it touches upon the new capabilities organizations need to build to govern AI effectively across its full lifecycle.
The session further addresses how to establish clear accountability for AI-driven decisions, design controls that embed human oversight, and create the evidence-based reporting that regulators, auditors, and boards increasingly expect. Attendees will leave with a practical leadership perspective on moving from AI principles to a measurable, actionable governance structure that supports responsible innovation, sustained trust, and long-term regulatory readiness.
Key Takeaways:
- Understanding responsible AI principles and how they translate into enterprise GRC practice
- Identifying the most significant AI risk categories and their implications for governance and compliance
- How existing GRC frameworks can be extended and adapted to govern AI systems across their full lifecycle
- Practical approaches to AI risk assessment, classification, control design, and ongoing monitoring
- Establishing clear ownership, accountability structures, and human oversight for AI-driven actions and decisions
- Building evidence-based AI governance programs that meet the expectations of internal auditors and external regulators
- How GRC and security leaders can enable responsible AI adoption while maintaining risk management discipline and stakeholder trust
Speaker:
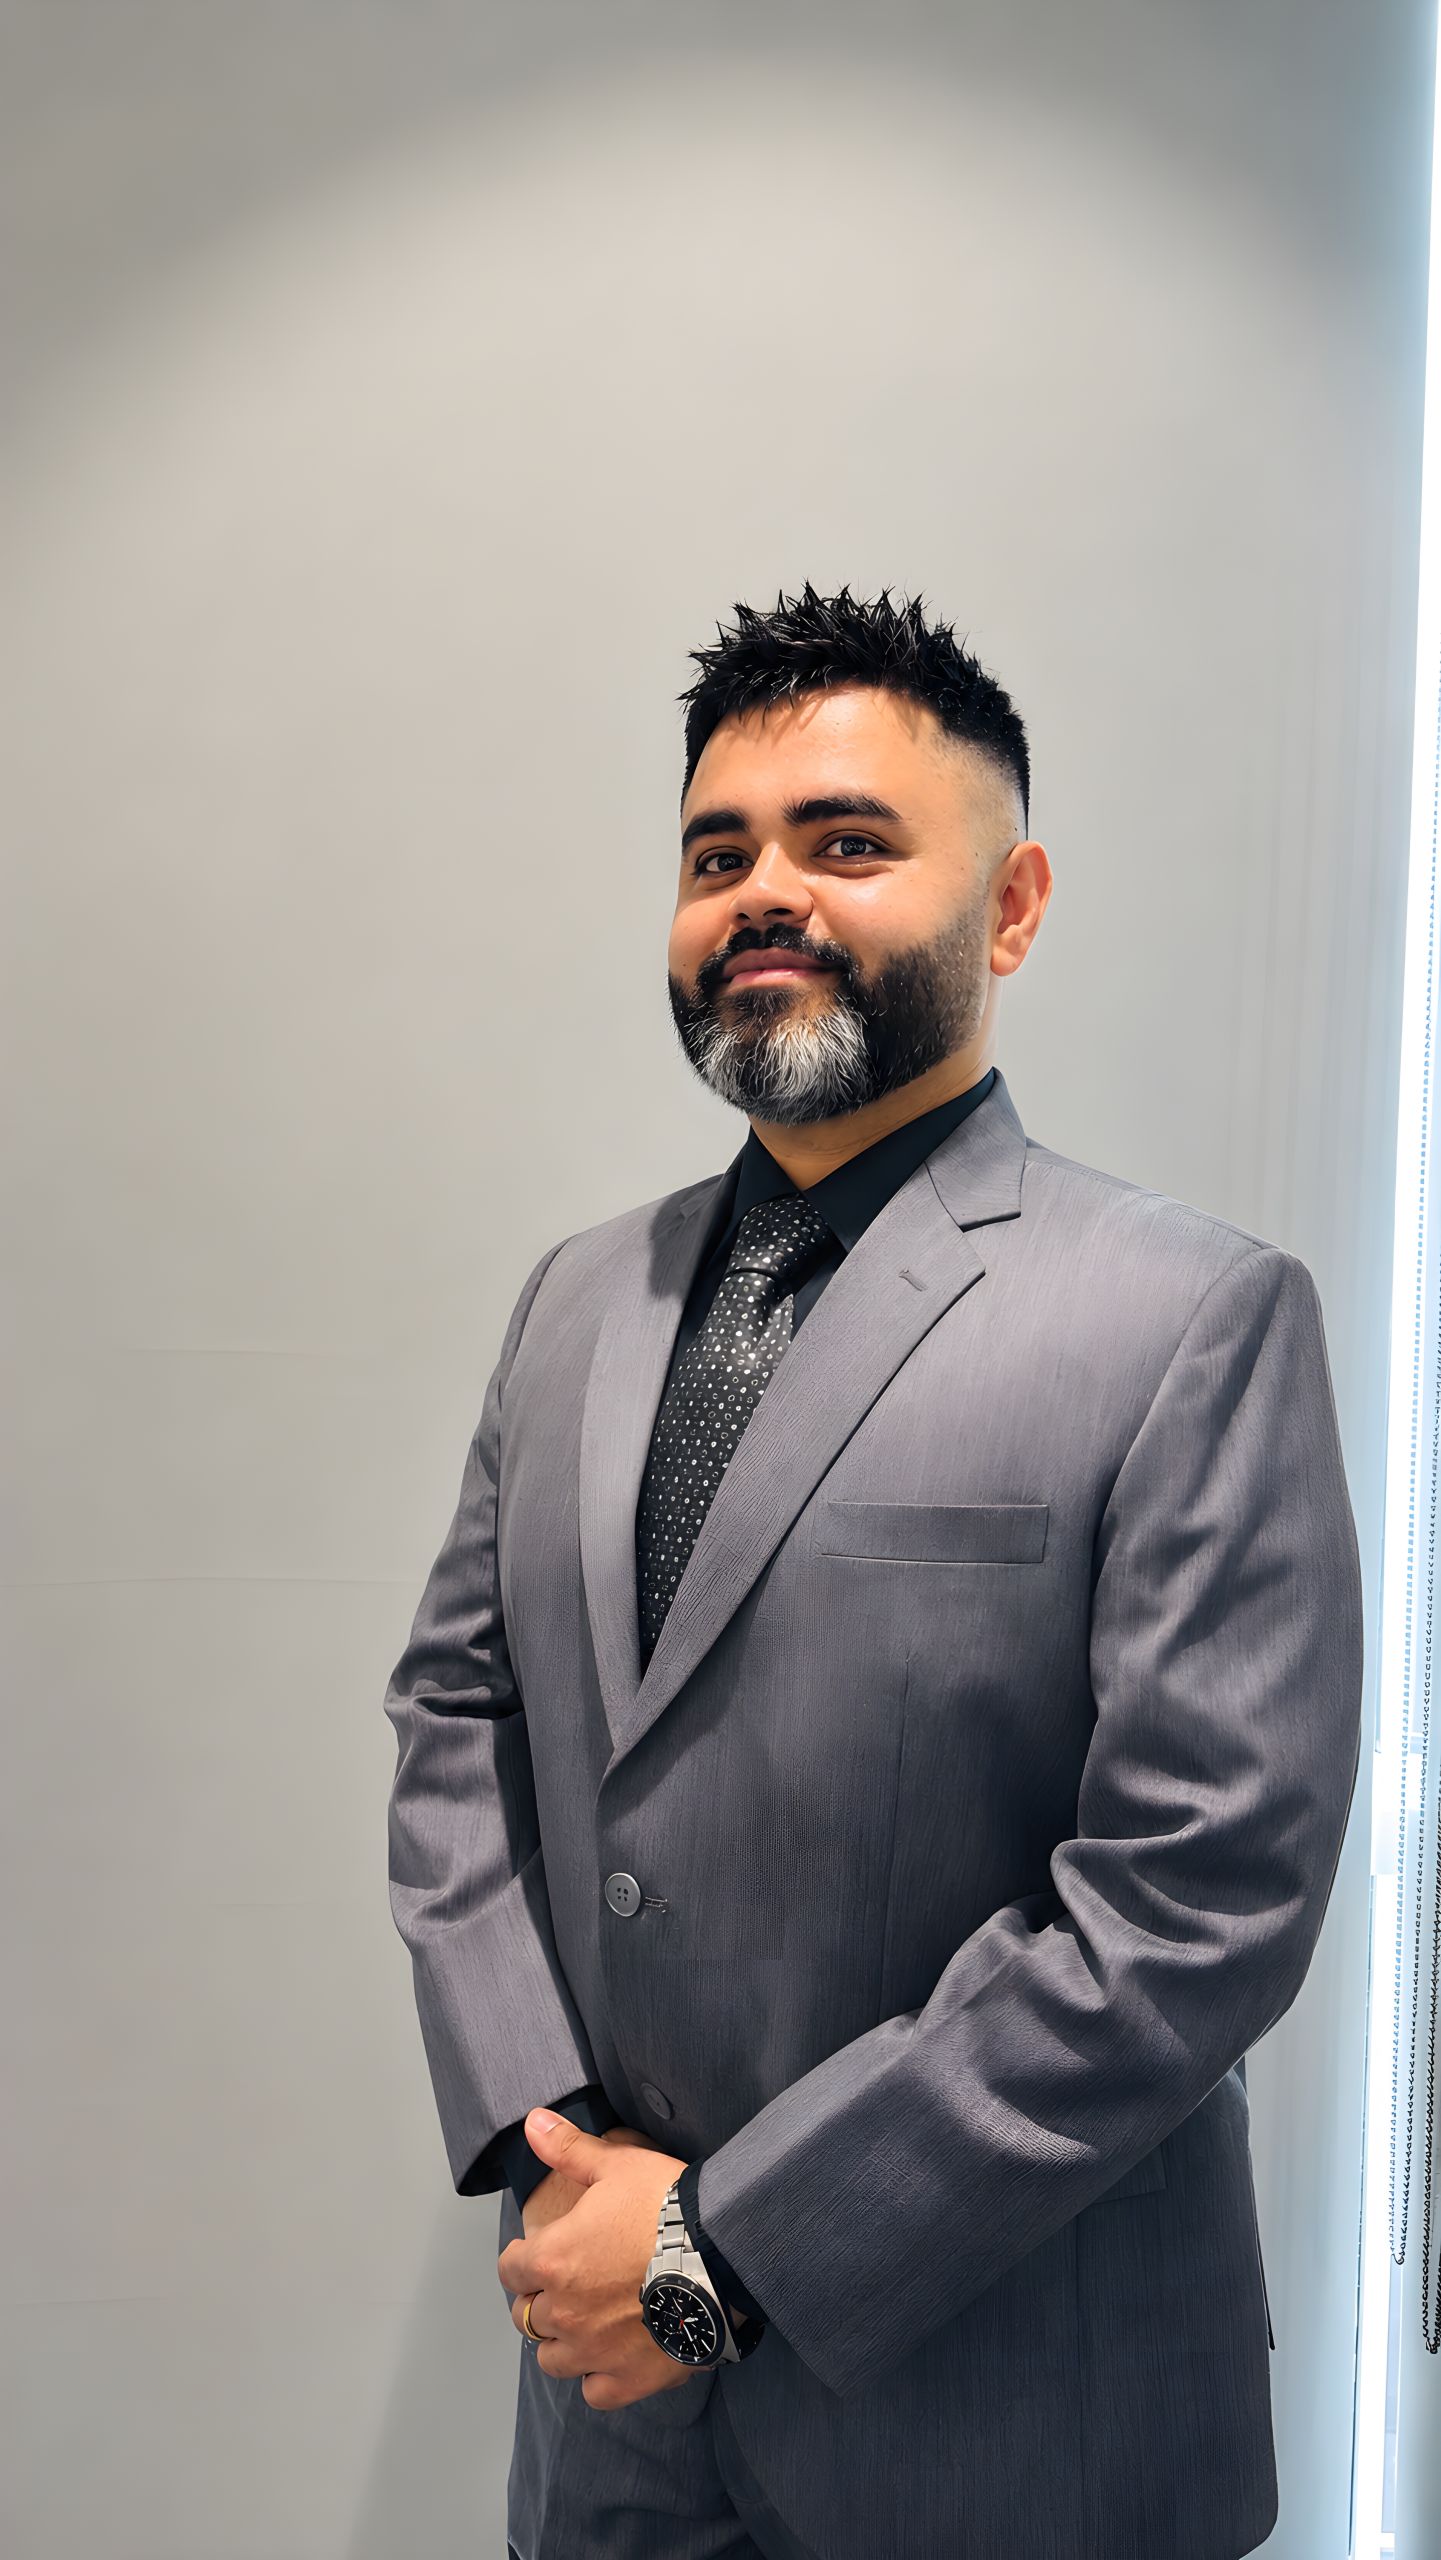 Joel Rosario Pereira, Cybersecurity Leader, International Organization in the BFSI Sector, Ex-Big Four consulting
Bio: Joel Pereira is a seasoned cyber, information security, and AI governance leader with more than 12 years of international experience driving cybersecurity governance, regulatory compliance, enterprise risk management, and responsible technology transformation.
With experience spanning leading global organizations including Deloitte, PwC, KPMG, and an international group in the BSFI sector, Joel has advised organizations across the Middle East in financial services, government, and other critical sectors. He brings a unique ability to bridge business strategy, technology, regulatory expectations, and cybersecurity governance.
Joel has led enterprise-wide initiatives covering information security strategy, NIST Cybersecurity Framework assessments, ISO/IEC 27001 certifications and SOC 2 attestations, regulatory engagement, cyber resilience, and security culture. More recently, he has been instrumental in establishing enterprise AI governance capabilities and alignment with regulatory expectations for the responsible adoption of AI.
He holds an MBA in Global Finance & Banking and a B.E. in Computer Engineering, along with globally recognized certifications including AIGP, CISSP-ISSMP, CISSP, CRISC, CCSP, CISM, CISA, PMP, various Microsoft certifications, and CDPSE.