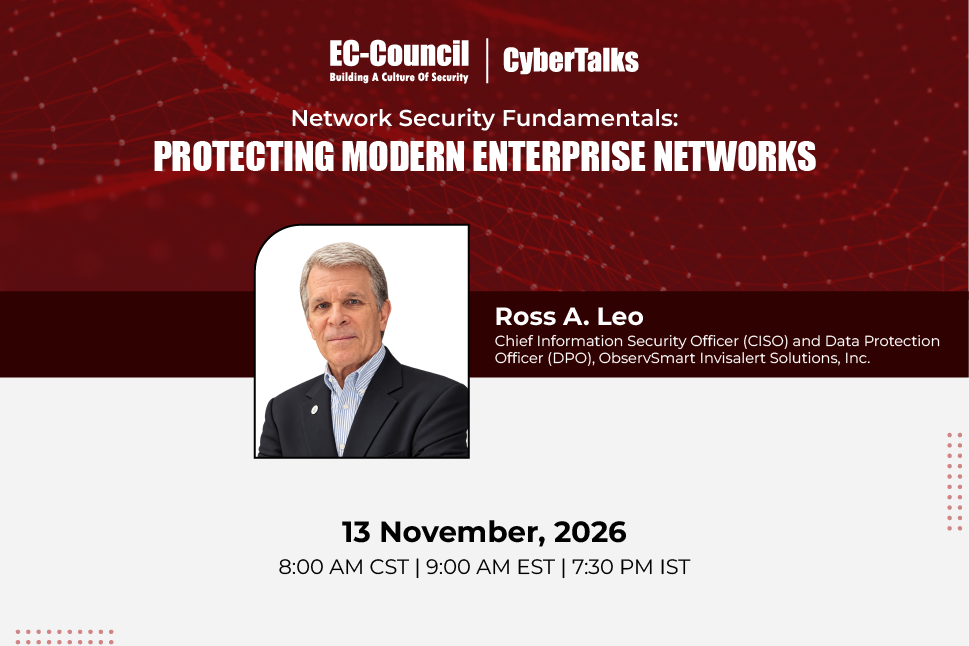
Topic: Network Security Fundamentals: Protecting Modern Enterprise Networks
Abstract: The modern enterprise network no longer has a defined edge. Cloud services, remote workforces, SaaS platforms, mobile endpoints, APIs, and interconnected environments have distributed the network across boundaries that traditional perimeter-based security was never designed to protect. Securing these environments requires a rethinking of foundational network security principles and how they are applied in practice.
This webinar examines network security fundamentals through the lens of today’s enterprise environments. It covers how organisations can approach network architecture, segmentation, access control, and secure connectivity in a way that reflects current threats and infrastructure realities. The session will also explore how Zero Trust principles, identity-centric security, and cloud networking are reshaping what network defence looks like.
Attendees will leave with a practical understanding of how to assess network risks, select and implement appropriate security controls, improve visibility across distributed environments, and build a defence-in-depth strategy designed for the complexity of modern enterprise technology.
Key Takeaways:
- Understanding enterprise network security architecture principles in the context of a changing attack surface
- Applying network segmentation and Zero Trust to strengthen modern network defence
- Integrating identity and access controls into a comprehensive network security approach
- Building network visibility, traffic monitoring, and threat detection capabilities that keep pace with evolving threats
- Preparing network security teams to detect, investigate, and respond to network-based incidents effectively
- Designing and implementing a defence-in-depth strategy suited to modern enterprise network environments
- Establishing continuous monitoring and security operations practices for sustained cyber resilience
Speaker:
 Ross A. Leo, Chief Information Security Officer (CISO) & Data Protection Officer (DPO), ObservSmart Invisalert Solutions, Inc.
Bio: Ross A. Leo is an information security pioneer with more than four decades in the field. His experience spans systems analysis and engineering, security and privacy consulting, operational risk, healthcare information governance, and professional education. His prior employers and engagements have included IBM, St. Luke’s Episcopal Hospital, Computer Sciences Corporation, and Rockwell International. During 22 years supporting NASA, he served from 1998 to 2002 as Program Manager of Security Engineering and Chief Security Architect for Mission Control at Johnson Space Centre. He later served from 2002 to 2006 as Director of Information Security and Chief Information Security Officer for the University of Texas Medical Branch Managed Care Division.
In addition to his extensive field experience, he has many years’ experience designing and teaching professional curricula in nearly every area of information security and has taught several thousand security and privacy practitioners. As a published author, he wrote and edited The HIPAA Program Reference Handbook for CRC Press in 2005. He co-authored NISTIR 8006, NIST Cloud Computing Forensic Science Challenges (2020), and NIST SP 800-201, Cloud Computing Forensic Reference Architecture (2024). His next book from CRC Press will be released in early 2027: ‘HIPAA Compliance: From Design to Operations’.