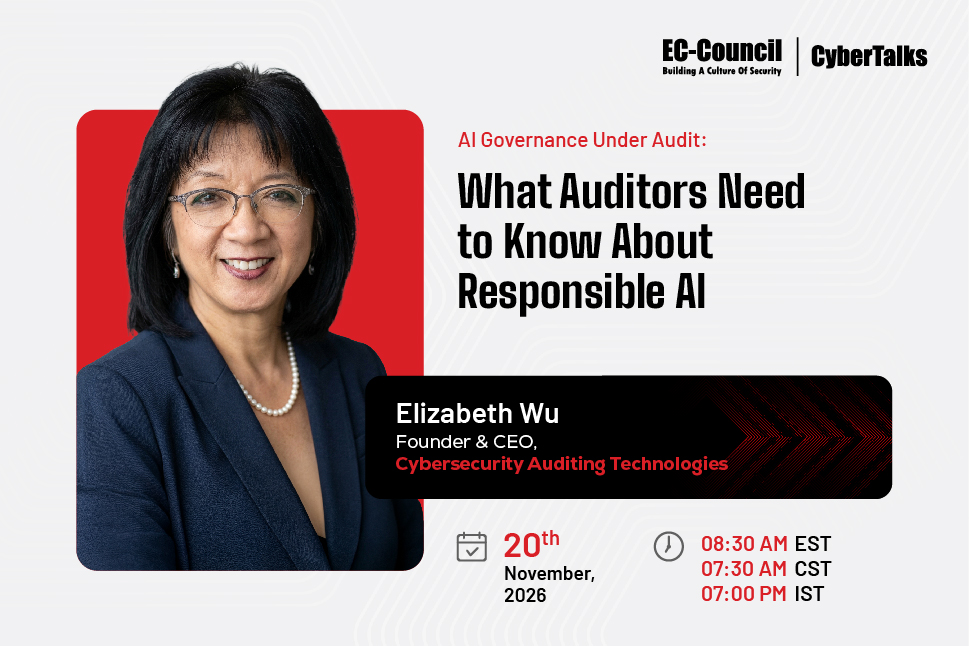
Topic: AI Governance Under Audit: What Auditors Need to Know About Responsible AI
Abstract: The rapid adoption of generative and agentic AI is creating new challenges for IT auditors and assurance professionals. As organizations integrate artificial intelligence into business operations and decision-making, auditors must understand how AI systems are governed, who is accountable for their use, and what evidence demonstrates that the associated risks are being managed.
Traditional auditing principles remain relevant, but AI introduces additional considerations involving model behavior, data lineage, third-party dependencies, transparency, human oversight, and autonomous decision-making.
This webinar examines AI governance through the lens of independent IT auditing, focusing on the distinction between what organizations report about their AI governance practices and what can be substantiated through objective evidence.
Participants will explore how recognized governance and risk management frameworks provide criteria for evaluating AI-related controls, identifying gaps, assessing accountability, and examining whether controls are operating as intended.
The discussion will also consider how auditors can move beyond reviewing policies and documented procedures to evaluating actual AI governance activities, along with supporting records, monitoring results, exceptions, and corrective actions.
The central question is straightforward: When an organization claims that its AI systems are responsibly governed, how do we know?
Key Takeaways:
- How generative and agentic AI are changing the scope of IT audit and assurance.
- The governance structures, responsibilities, and accountability mechanisms auditors should examine.
- How recognized frameworks can provide criteria for assessing AI governance controls.
- How to evaluate evidence concerning AI data governance, model risk, security, transparency, and human oversight.
- The distinction between documented policies, reported activities, and independently examined evidence.
- How to identify AI governance exceptions, control weaknesses, and gaps requiring further investigation.
- What audit-ready evidence looks like and how audit findings can support informed organizational decisions.
Speaker:
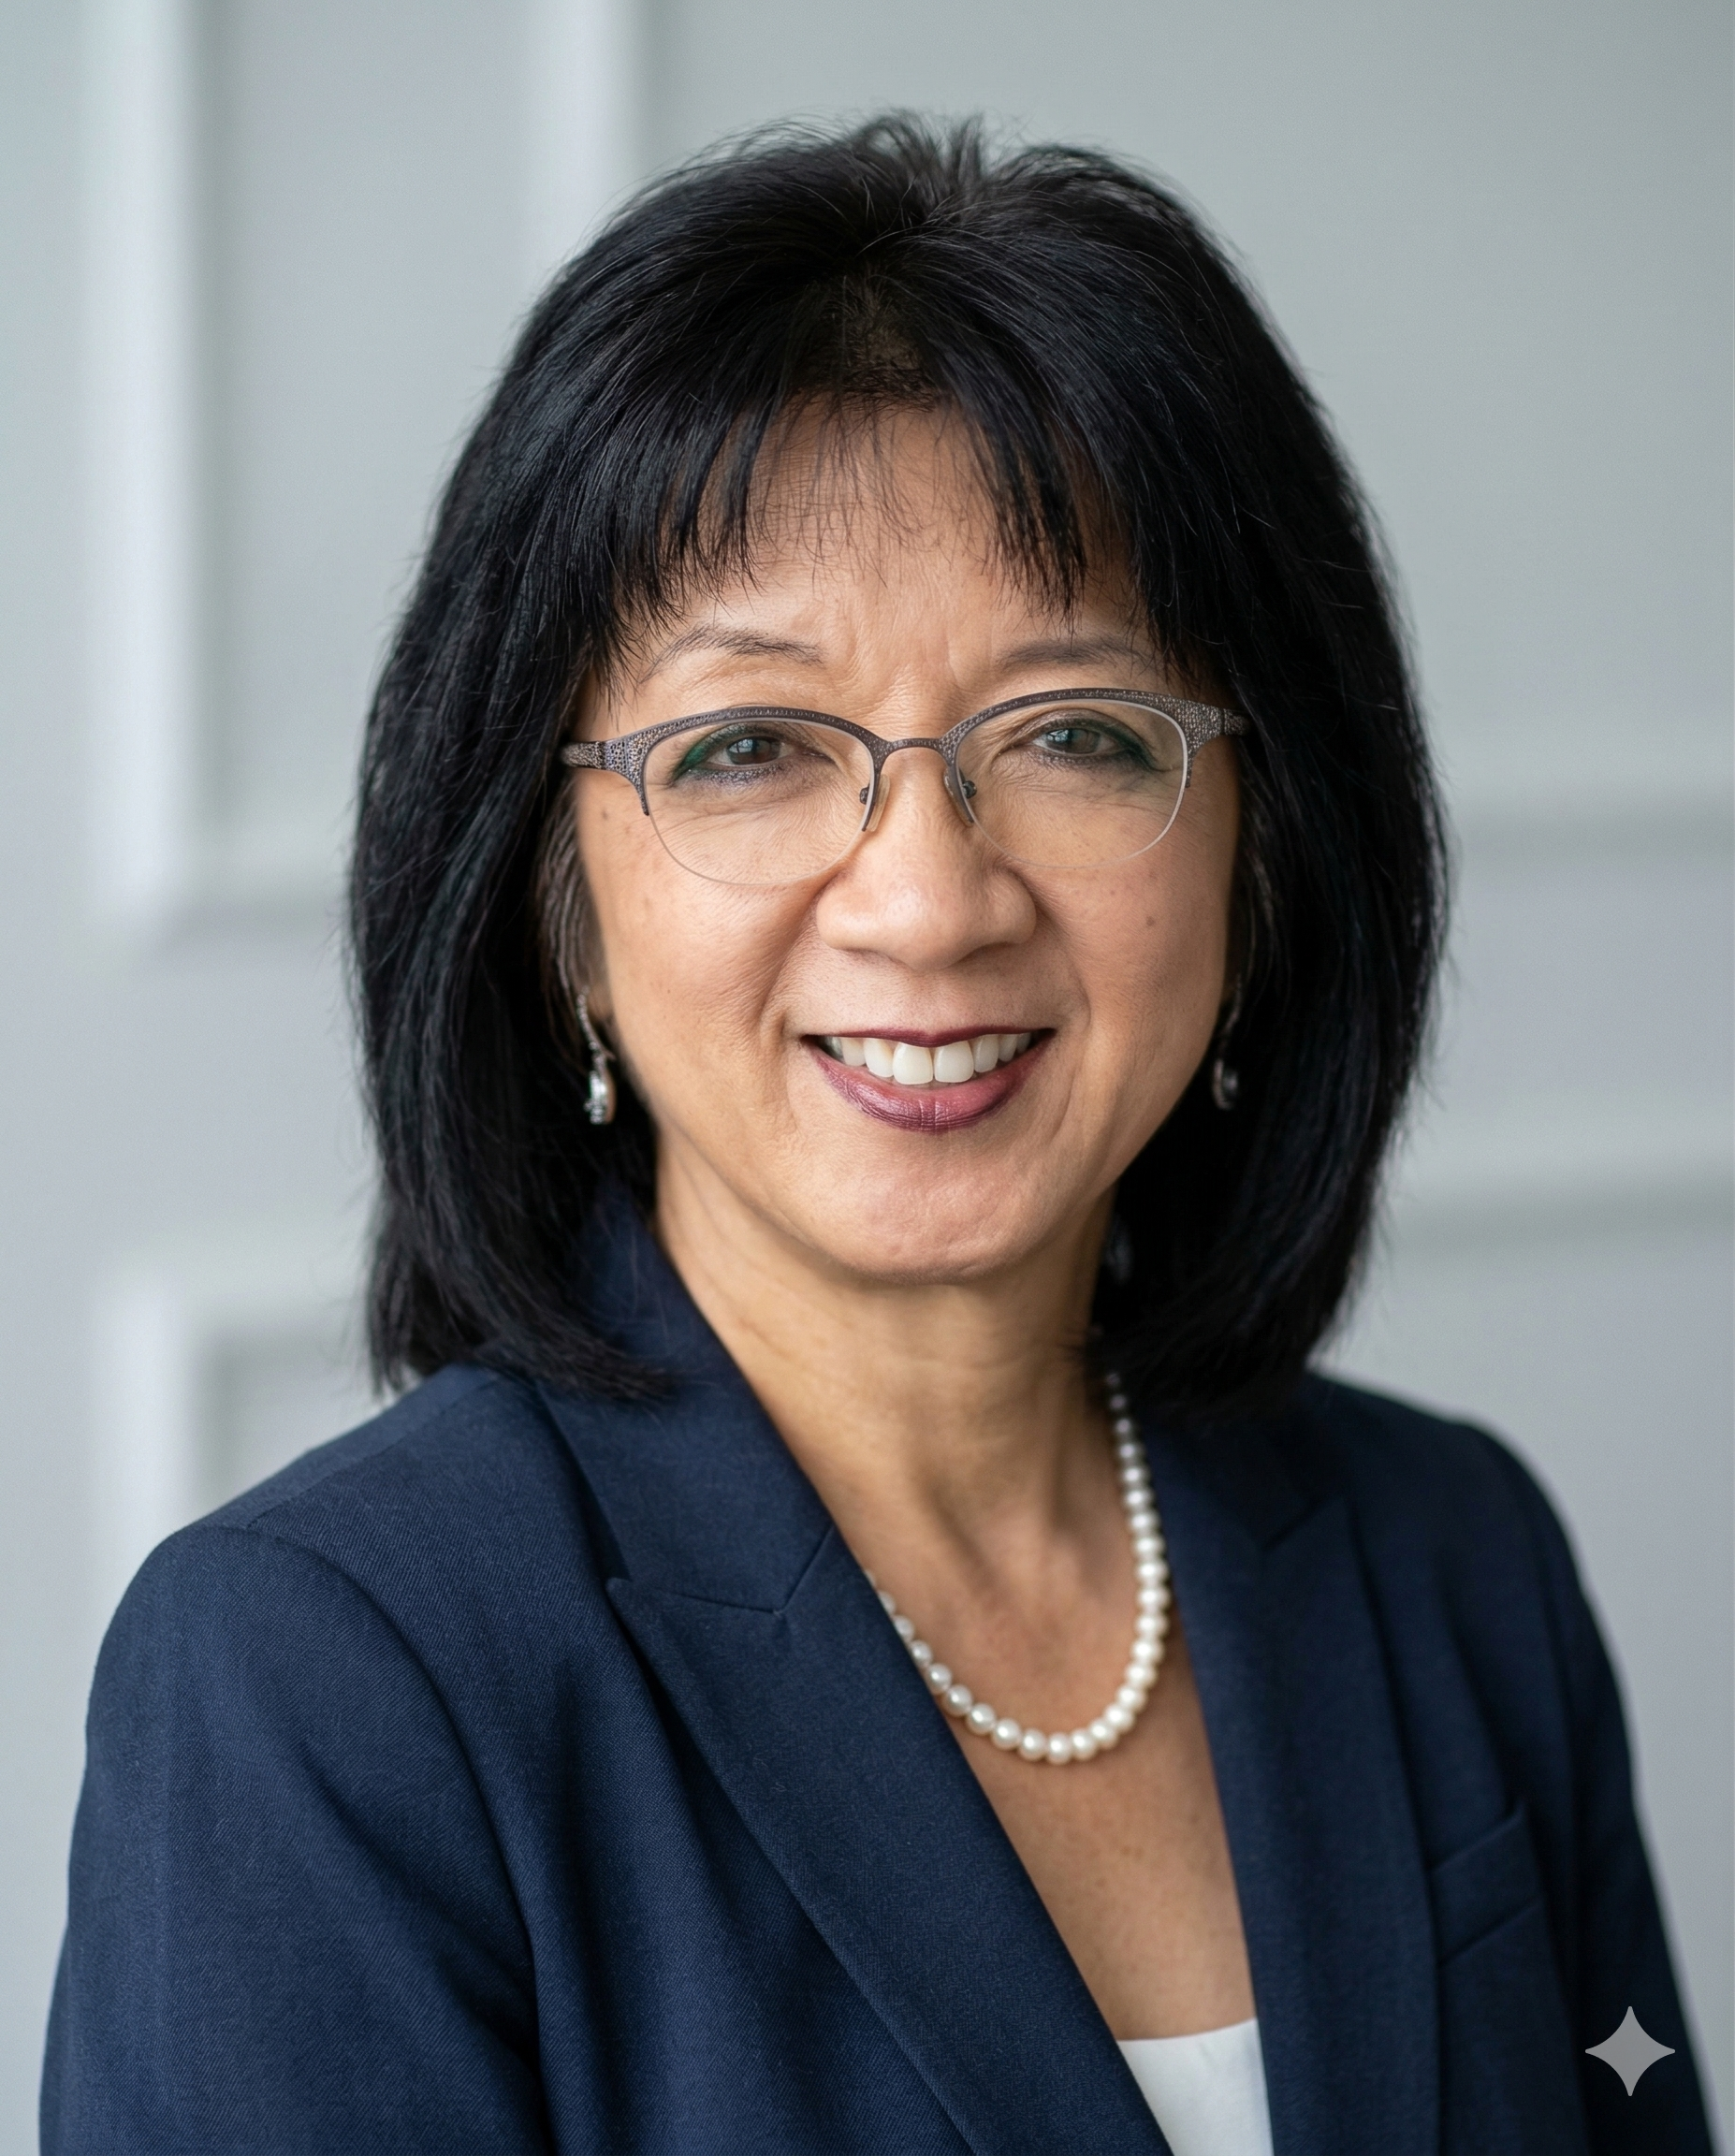 Elizabeth Wu, Founder & CEO, Cybersecurity Auditing Technologies
Bio: Elizabeth Wu is the Founder and CEO of Cybersecurity Auditing Technologies, an IT security auditor, consultant, and author with more than 25 years of experience working with technology, cybersecurity, and organizational risk.
A contributor to the Center for Internet Security (CIS), her work focuses on the gap between what organizations believe about their cybersecurity and what can actually be demonstrated through independent examination and objective evidence.
Elizabeth works with executives and organizations to strengthen cyber governance, accountability, and evidence-based oversight. She is the author of The Illusion of Cyber Governance: Why Proof Matters More Than Protection, which examines why organizational confidence does not always correspond with demonstrable security.
Her current work applies these same principles of accountability, independent examination, and evidence-based assurance to AI governance and emerging technology risks.